Critical Windows “MS-NRPC” Exploit ZeroLogon (CVE-2020-1472)

About

Microsoft issued a security update guide on August 11, 2020 and a security patch for a critical vulnerability in Microsoft Netlogon Remote Protocol “MS-NRPC“ that allows attackers to gain domain administrator access to the Active Directory server and perform malicious activities.

The vulnerability was discovered by Secura’s security expert Tom Tervoort and it was given the highest rating score. (CVSS score: 10.0)
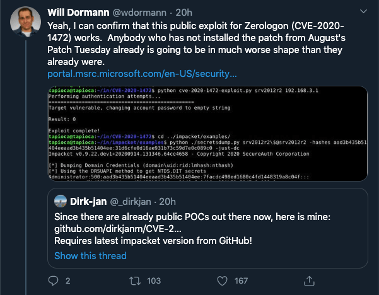
Exploits and proof of concept are currently available with reports that the vulnerability is being exploited in the wild.
What Does This Mean to our Partners?

Any attacker with any unauthenticated access to the domain controller can exploit this vulnerability and escalate his/her privilege to become a domain admin with just one click.

Mitigation

Install the Microsoft August Tuesday update which will fix this vulnerability in the server by enforcing RPC in the Netlogon protocol for all windows devices.

As Microsoft said: “A security update was released in August 2020. Customers who apply the update, or have automatic updates enabled, will be protected.”

Get More Information

DATE PUBLISHEDSeptember 16, 2020
AUTHORBlackpoint Cyber

The Cost of Waiting

The Cost of Waiting: What Identity Attacks Cost the MSP ebook What Identity Attacks Cost the MSP Stolen credentials don't trip alarms. Once an attacker is authenticated, they look like anyone else, and most tools aren't watching what happens next. Learn what closing the identity response gap looks like: how identity attacks happen, where response slows down, and the questions to ask any ITDR vendor.
*Identity-based techniques play a role in nearly 90% of incident investigations

GET YOUR COPY